

From Assessment to Enforcement: A Practical Path to Securing the AI Agents Inside Your Enterprise
Nov 12, 2026 8:00 AM PST
Head of Innovation
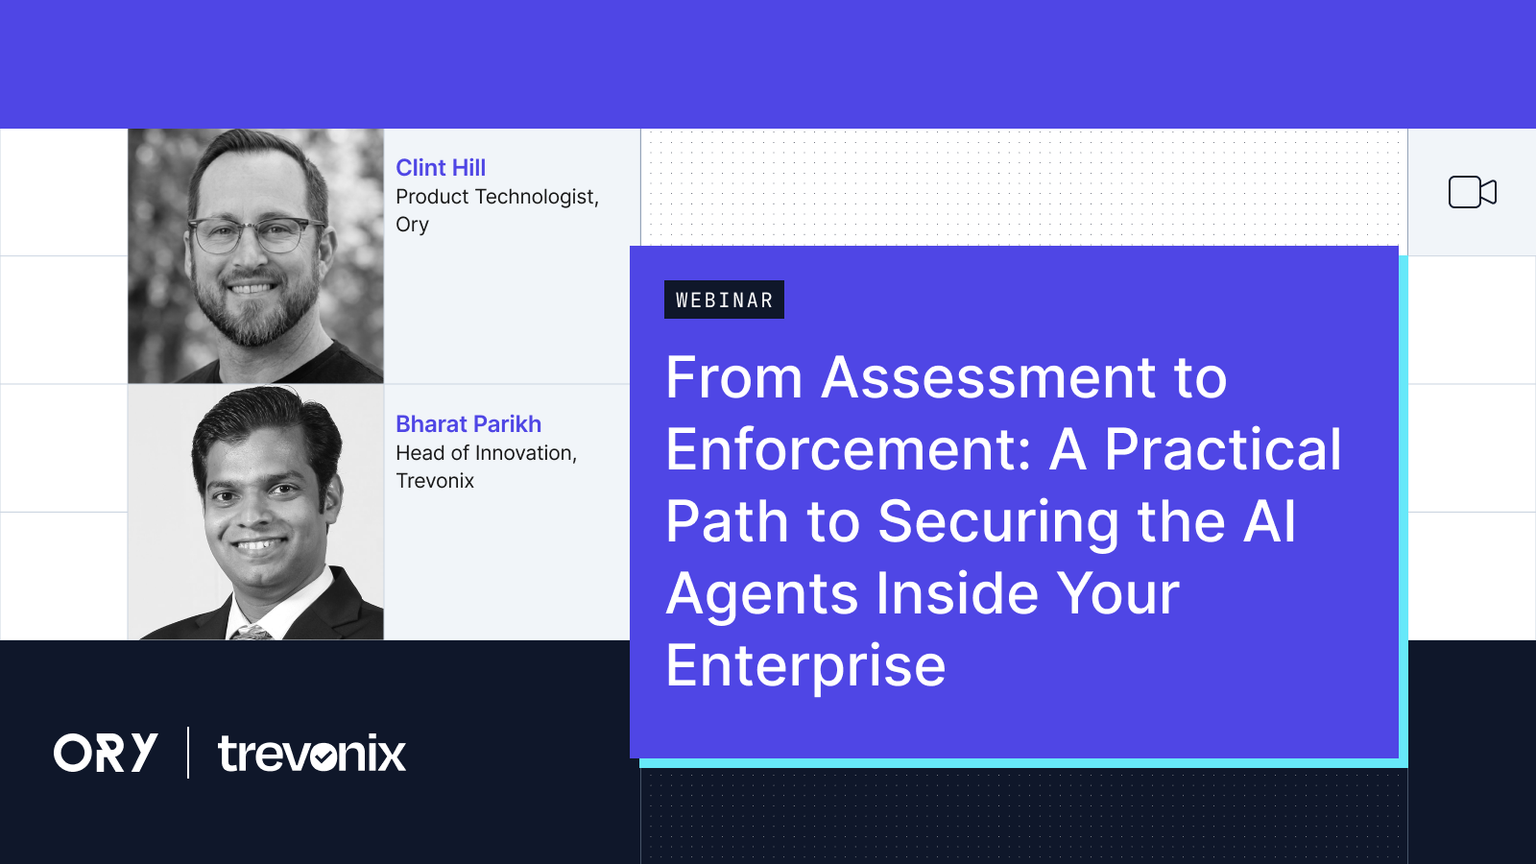
AI coding agents and workforce agents now work inside the enterprise with the same access as the employees who launched them, including code repositories, cloud environments, business systems, and sensitive data. Most identity and security programs were built to govern people and service accounts. As a result, many organizations can’t say what each agent is doing, which actions it should be allowed to take, or how to stop it when something goes wrong. In this session, Trevonix and Ory walk through what changes when agents join your workforce. Trevonix maps the current agent landscape and shares real-world cases where adoption went wrong, along with the identity and access lessons each one teaches. Controls placed in front of an agent, such as gateways and proxies, only see the traffic that passes through them, and agents regularly find a path around them. Ory moves the check to the point of action, so an agent might take a new route but cannot skip the authorization. While Ory enforces guardrails, Trevonix defines who owns the decisions. Together, Trevonix and Ory connect policy, accountability, and enforcement, so agents can be governed, monitored, and stopped when needed. You’ll see a live demonstration of guardrails on a coding agent and how to introduce guardrails without slowing developers down. Each action is traced to the agent that took it, risky actions are blocked before they run, and access is cut off in real time. Who should attend: CISOs, IAM leaders, security architects, platform and engineering teams, and anyone who owns AI governance. You’ll leave with: - A clear picture of which agent types carry the most risk, and why - The ownership, governance, and monitoring questions to settle before you scale agents - A path from a one-time assessment to guardrails that keep running - A live look at trending agent use cases