

Ory’s Response to the Java4Shell (CVE-2026-114938) Vulnerability
Ory Network, Ory Enterprise License (OEL) and self-hosted Ory aren’t affected by Java4Shell, the OpenJDK Base64 heap overflow. This page tracks our status and sub-processor review.

Further reading

We're tracking several recently disclosed vulnerabilities, including the eMudhra certificate compromise and CVEs in PHP, Go, and Node.js. This page lists Ory's status for each one and will be updated as we learn more.
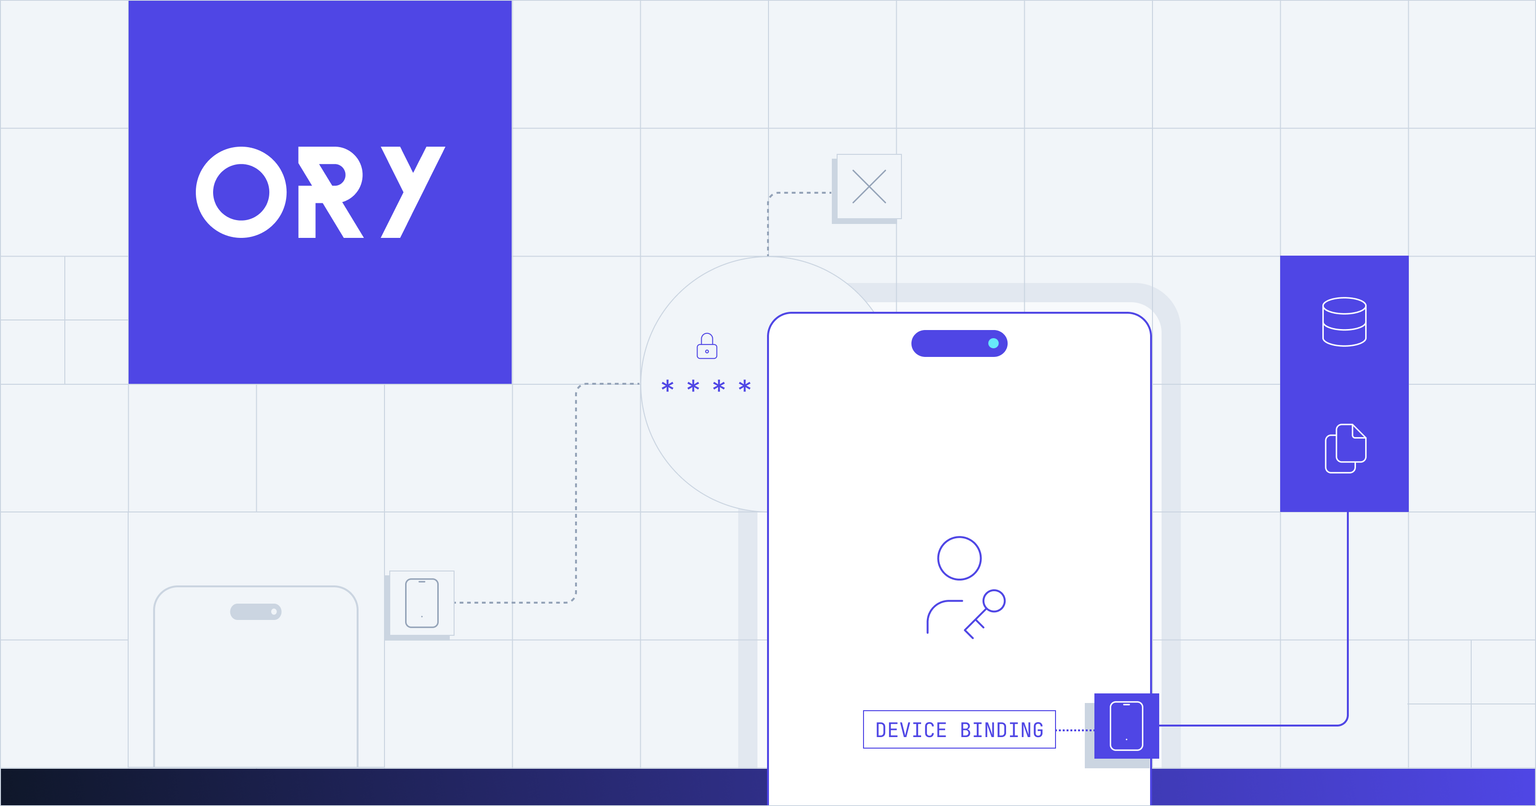
Most authentication proves someone holds the right credential, not which device they're holding it on. Device binding (also called device authentication) closes that gap: a private key generated in a phone's secure hardware, attested by Apple or Google, and used for step-up approval or full passwordless login via PIN or biometrics.
Introducing Ory Agent Security — authentication, authorization, and audit for the AI coding agents now working across your engineering org.
When AI agents generate millions of auth requests per second, traditional identity infrastructure breaks. Learn how Ory and CockroachDB solve agentic scale.