We are happy and proud to announce that from today Ory Network is ISO 27001
certified by BARR.
This certification demonstrates that Ory has been thoroughly audited and found
to meet the standards set by the International Organization for Standardization
(ISO). In this blog post, we will explore why this achievement is significant
not only for us, but also for our customers and how it benefits them.
ISO 27001 is a widely recognized standard that specifies the requirements for
establishing, implementing, maintaining, and continually improving an
Information Security Management Systems (ISMS). The standard provides a
systematic approach to managing sensitive company information and mitigating the
risk of security breaches. ISO 27001 certification is recognized globally, and
compliance with the standard is often required as a prerequisite for doing
business.
Benefits
For our customers, the ISO 27001 certification offers several benefits:
It provides assurance that Ory’s ISMS meets internationally recognized best
practices for information security management. The certification
demonstrates that we have implemented comprehensive controls and processes
to protect our customers' data from threats such as cyberattacks, data
breaches, and theft.
This certification also helps our customers meet their own compliance
obligations. By working with a certified vendor, our customers can show
auditors and regulators that they have taken appropriate measures to protect
sensitive information. This can be particularly important for businesses
that handle personal data or operate in regulated industries, such as
healthcare, finance or government.
It reflects our commitment to transparency and accountability. The
certification process involves rigorous third-party auditing, which ensures
that Ory's security controls and processes have been independently verified.
This provides our customers with greater visibility into Ory's security
practices and helps build trust and confidence in the company's services.
Summary
In summary, achieving ISO 27001 certification is a significant milestone for us
and our customers. The certification demonstrates our commitment to information
security and provides customers with assurance that their data is being managed
in a secure and compliant manner. By working with a certified vendor, our
customers can meet their own compliance obligations, improve their security
posture and build trust with their own customers. Overall, ISO 27001
certification is a testament to our dedication to providing secure and reliable
services.
Outlook
But we will not stop here! For our commitment to continuously improve our
information security practices and provide a leading privacy-focused user
management infrastructure, we are currently working towards obtaining SOC2 Type
2 attestation, another widely recognized standard for information security
management and also release new Data Regionality features.
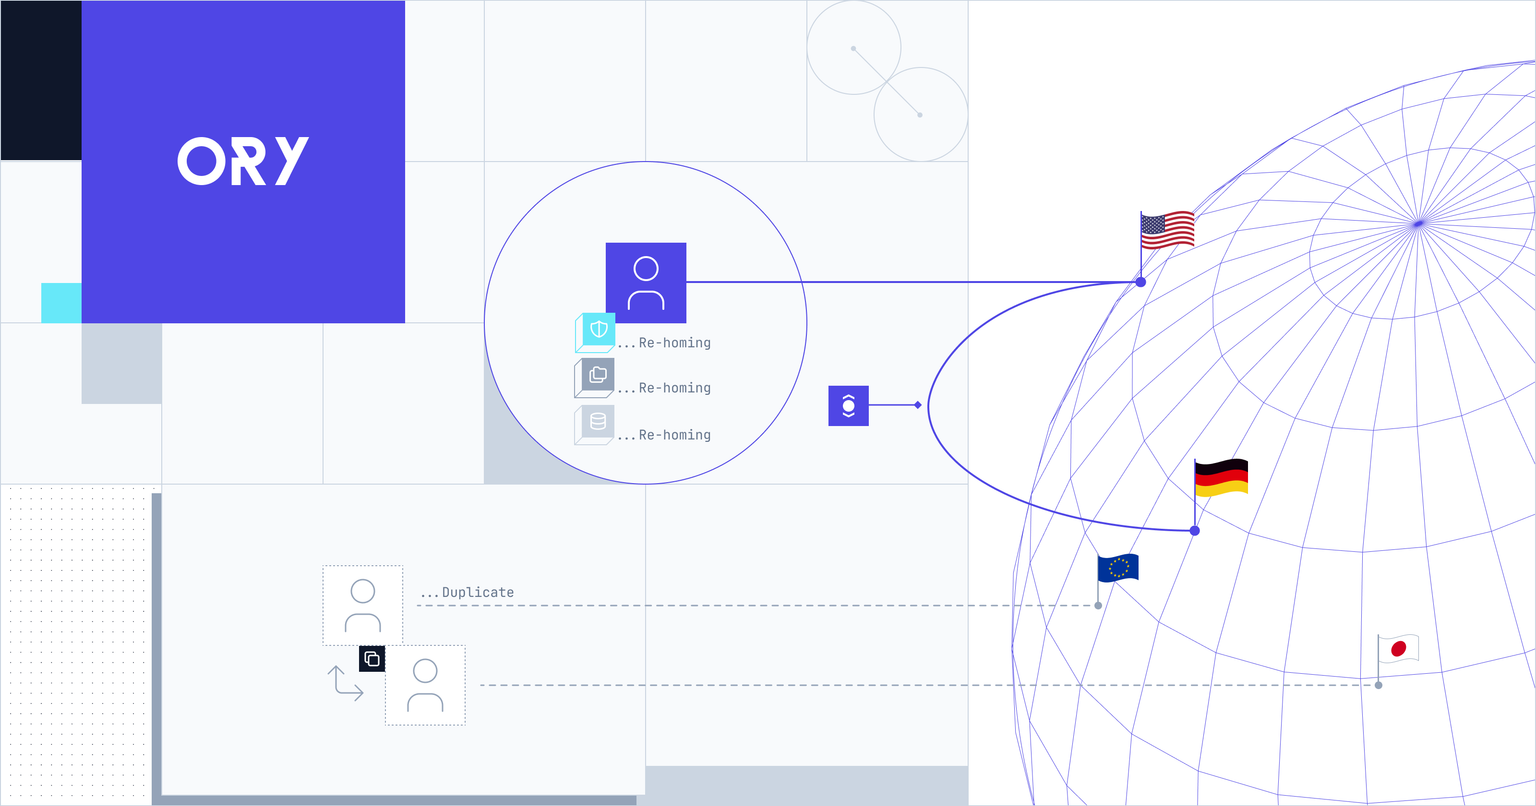
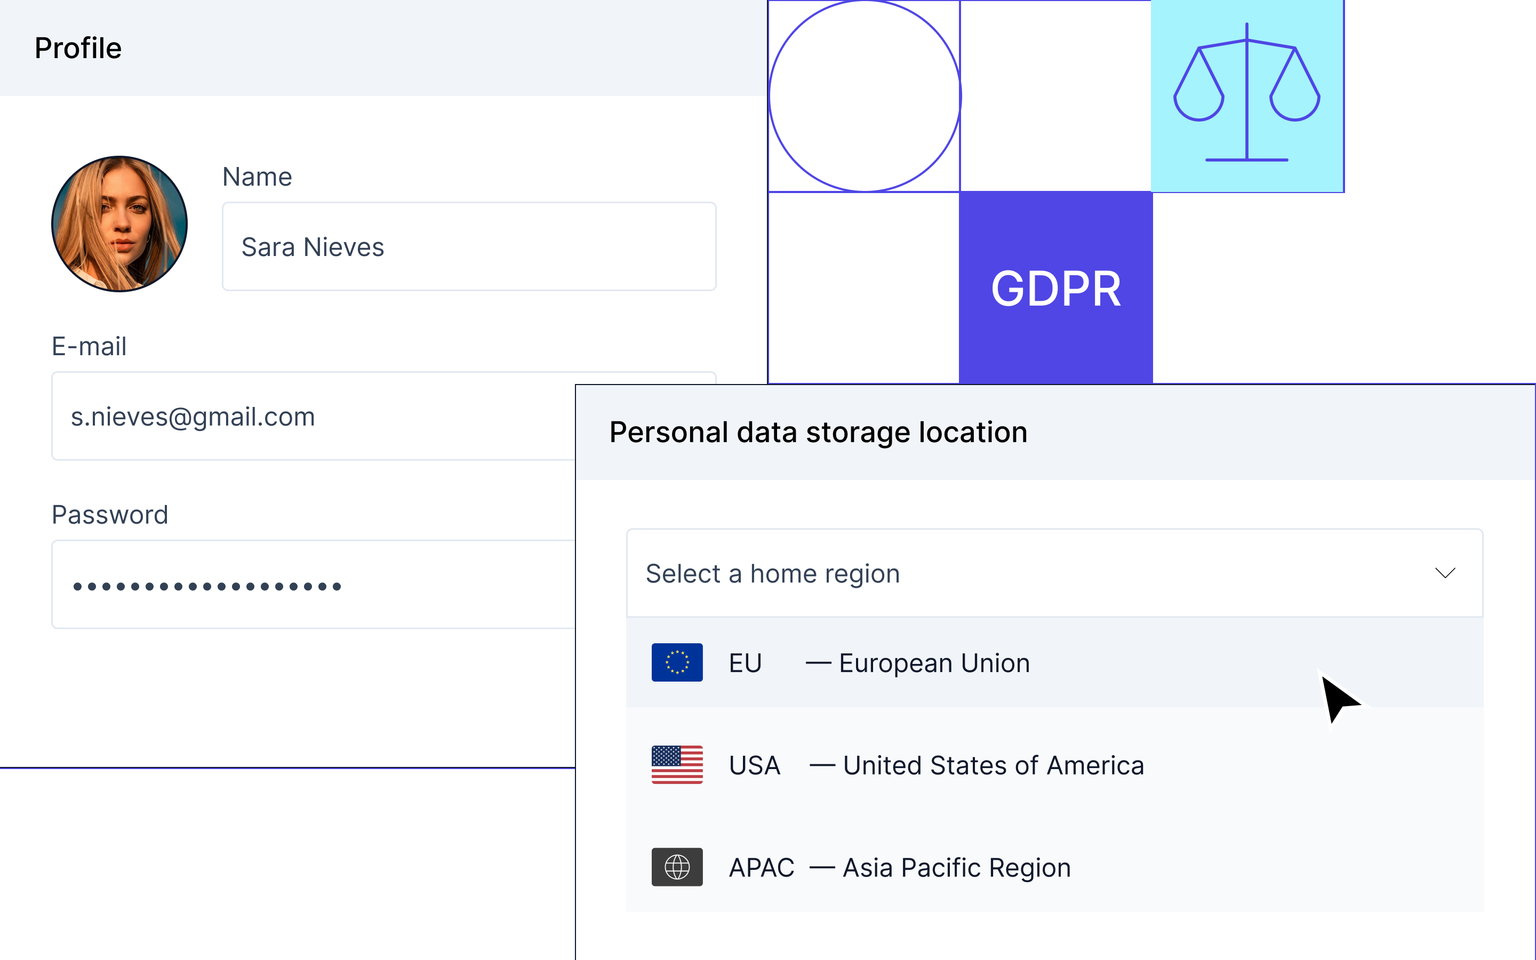
Data Regionality will allow our customers to choose the geographical location
where their data is stored, providing them with greater control and improved
performance over their data and helping them meet regional compliance
requirements as defined by the EU’s GDPR and California’s CCPA. We believe that
this will be also a very valuable addition to our Ory Network services and we
look forward to sharing more details with you soon.
Ory is now SOC 2 Type 2 compliant. Read more about it
here.